Ready to let ISO 27001 be someone else's problem?
Chat to one of our experts and see how we can take information security off your plate.

The simple way to get certification-ready, with a dedicated expert building the right controls and keeping them in place as you scale.
ISO 27001 is the internationally recognised standard for information security management. It sets out how a business manages its risks and keeps the right controls in place.
For some, it’s a requirement, enterprise clients and tenders won’t sign without it. For others, it’s a way to show customers and investors they take information security seriously.
But getting these controls in place can be a challenge, especially when it’s just one of many things on your plate.
We build an information security management system that’s sized for your business, not a generic template stretched to fit.
We take the heavy lifting off your plate: from gap analysis through to audit, so you can keep running the business while the controls get put in place.
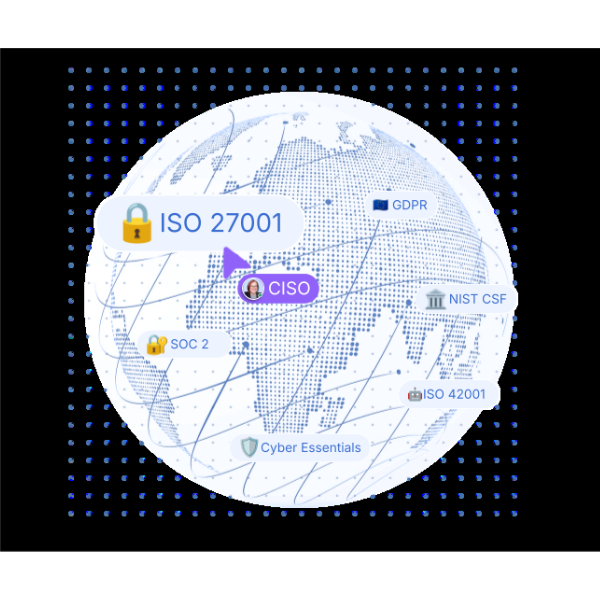

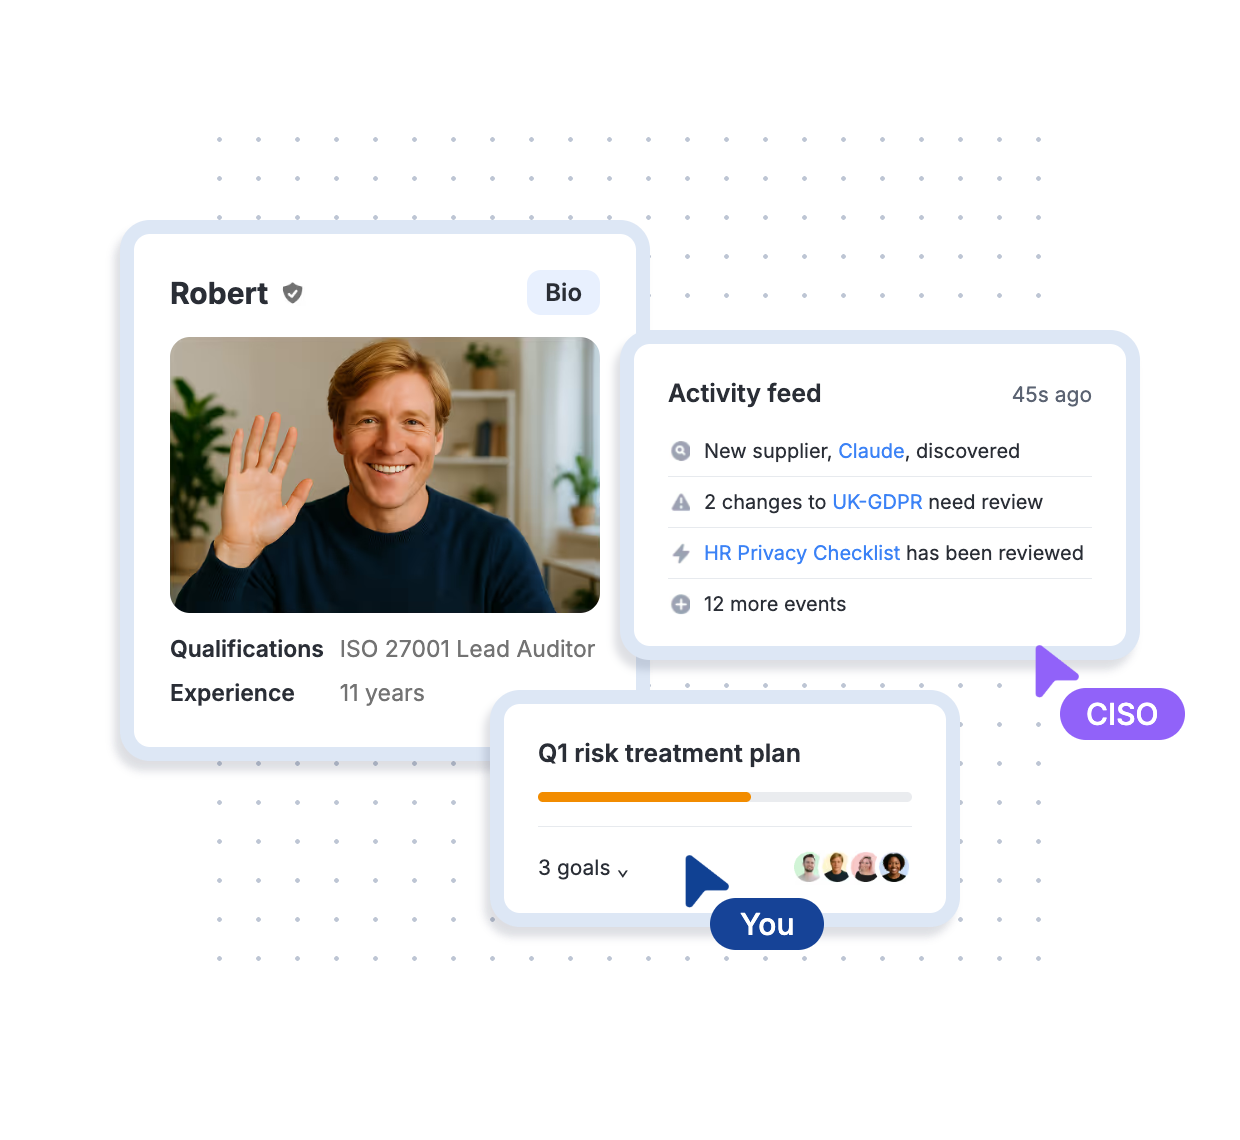
Our platform structures your ISO 27001 programme from day one, making it simple to evidence progress, track controls and collaborate as a team.
It does the heavy lifting behind the scenes, embedding good InfoSec practice into your everyday workflows, so you’re always ready to prove compliance to customers, investors and auditors.
You’re matched with a qualified ISO 27001 specialist who gets to know your business and guides you through every stage, from scoping to certification.
They become embedded in your business, bringing senior expertise, driving a stronger InfoSec culture, and taking the day-to-day work off your plate.
Chat to one of our experts and see how we can take information security off your plate.
Josephine Robinson, Information Security Director at Codat
Alisa Padhiar, Finance Director at Thortful
Caitlin O'Connell, Senior Business Partner at Ocean Bottle